
Export limit exceeded: 237727 CVEs match your query. Please refine your search to export 10,000 CVEs or fewer.
Export limit exceeded: 24327 CVEs match your query. Please refine your search to export 10,000 CVEs or fewer.
Search
Search Results (24327 CVEs found)
| CVE | Vendors | Products | Updated | CVSS v3.1 |
|---|---|---|---|---|
| CVE-2025-30314 | 1 Adobe | 1 Connect | 2025-05-19 | 6.1 Medium |
| Adobe Connect versions 12.8 and earlier are affected by a stored Cross-Site Scripting (XSS) vulnerability that could be abused by an attacker to inject malicious scripts into vulnerable form fields. Malicious JavaScript may be executed in a victim’s browser when they browse to the page containing the vulnerable field. | ||||
| CVE-2024-7313 | 1 Getshieldsecurity | 1 Shield Security | 2025-05-17 | 6.1 Medium |
| The Shield Security WordPress plugin before 20.0.6 does not sanitise and escape a parameter before outputting it back in the page, leading to a Reflected Cross-Site Scripting which could be used against high privilege users such as admin. | ||||
| CVE-2024-10893 | 1 Wpbookingcalendar | 1 Wp Booking Calendar | 2025-05-17 | 4.8 Medium |
| The WP Booking Calendar WordPress plugin before 10.6.5 does not sanitise and escape some of its settings, which could allow high privilege users such as admin to perform Stored Cross-Site Scripting attacks even when the unfiltered_html capability is disallowed (for example in multisite setup). | ||||
| CVE-2025-4547 | 1 Senior-walter | 1 Web-based Pharmacy Product Management System | 2025-05-16 | 2.4 Low |
| A vulnerability was found in SourceCodester Web-based Pharmacy Product Management System 1.0. It has been rated as problematic. Affected by this issue is some unknown functionality of the component Add User Page. The manipulation leads to cross site scripting. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. Multiple parameters might be affected. | ||||
| CVE-2024-26152 | 1 Humansignal | 1 Label Studio | 2025-05-16 | 4.7 Medium |
| ### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 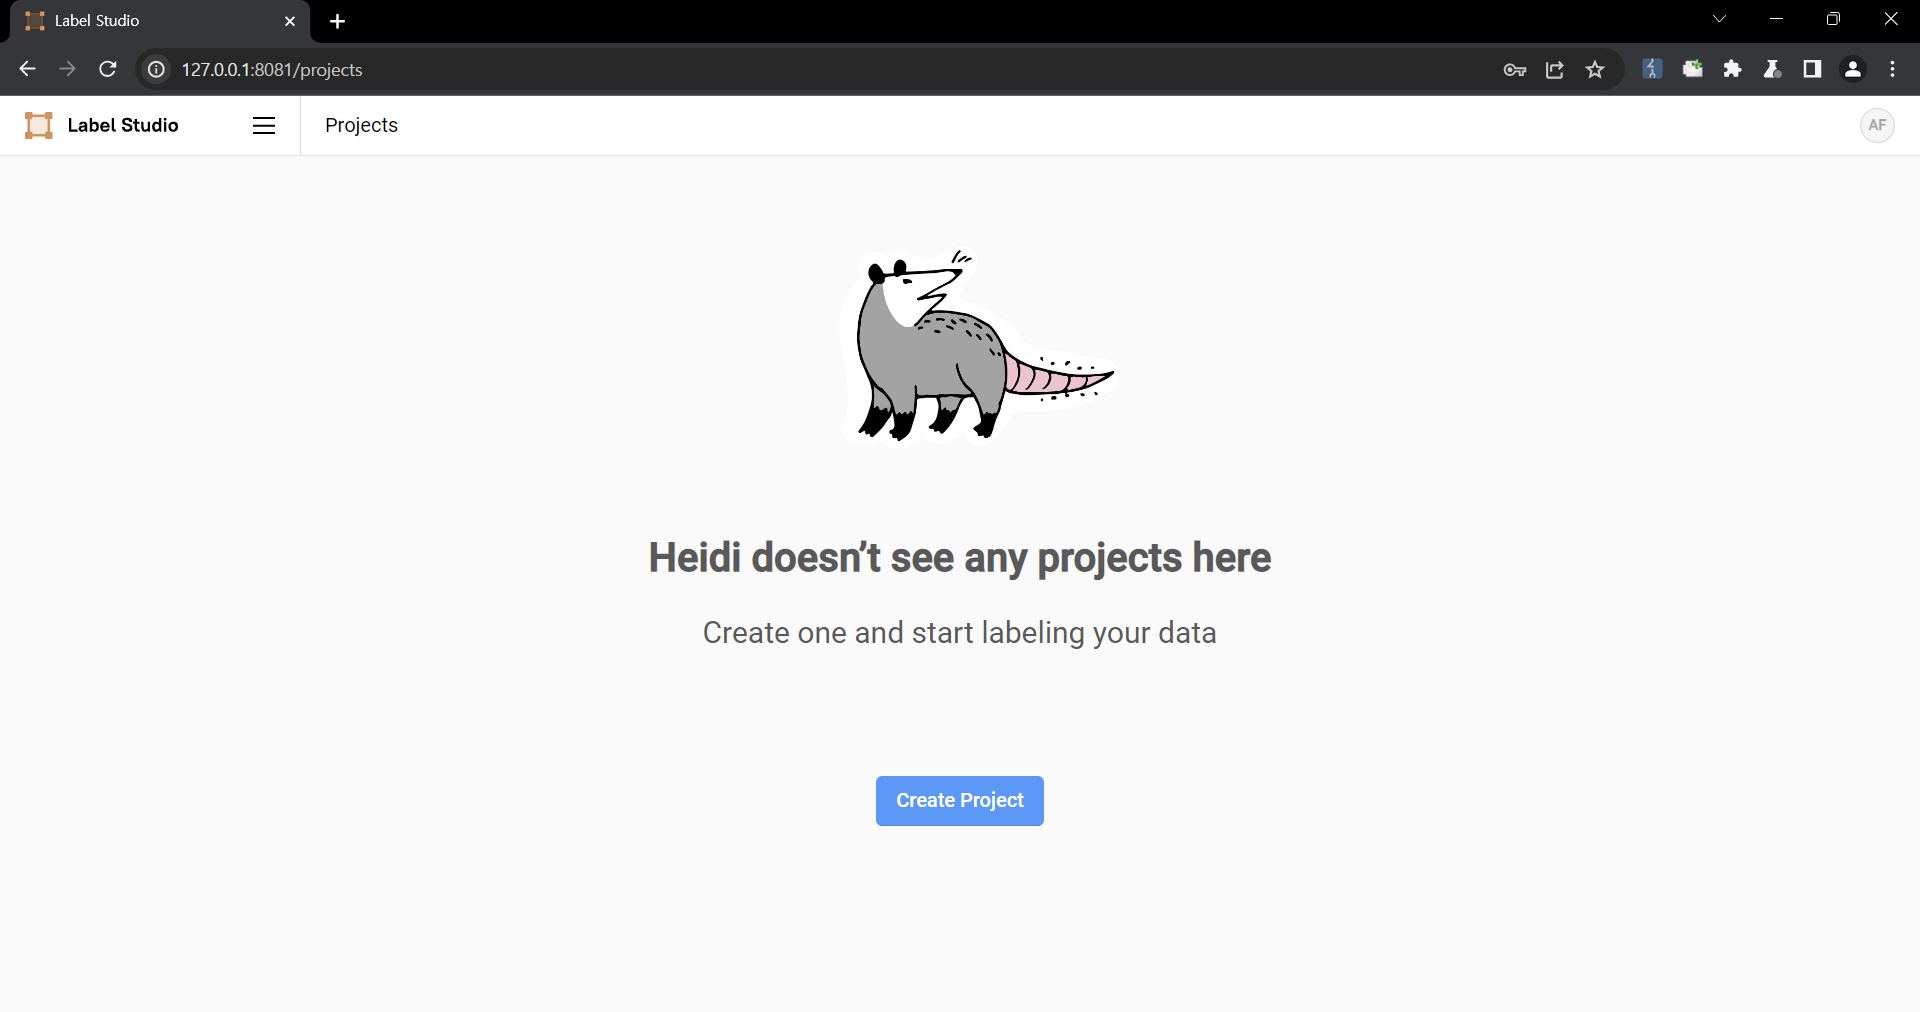 2. Upload a file containing the payload using the "Upload Files" function. 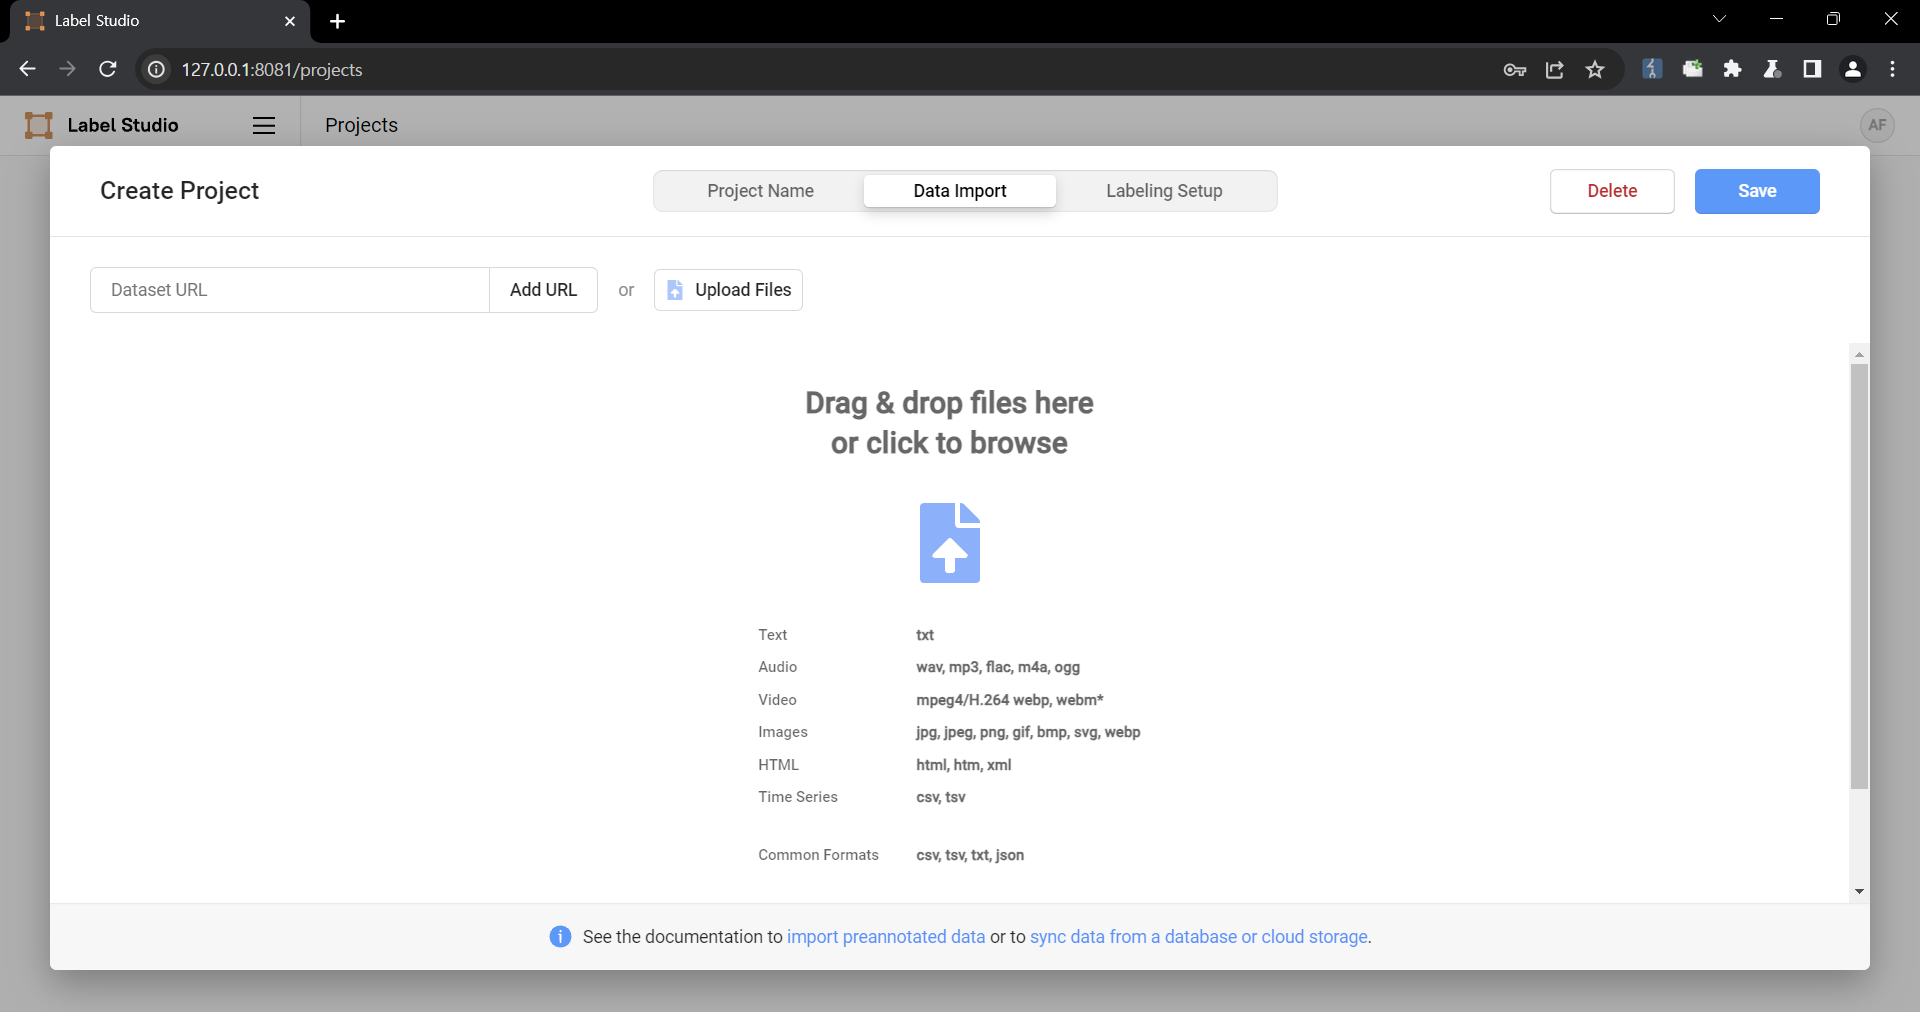 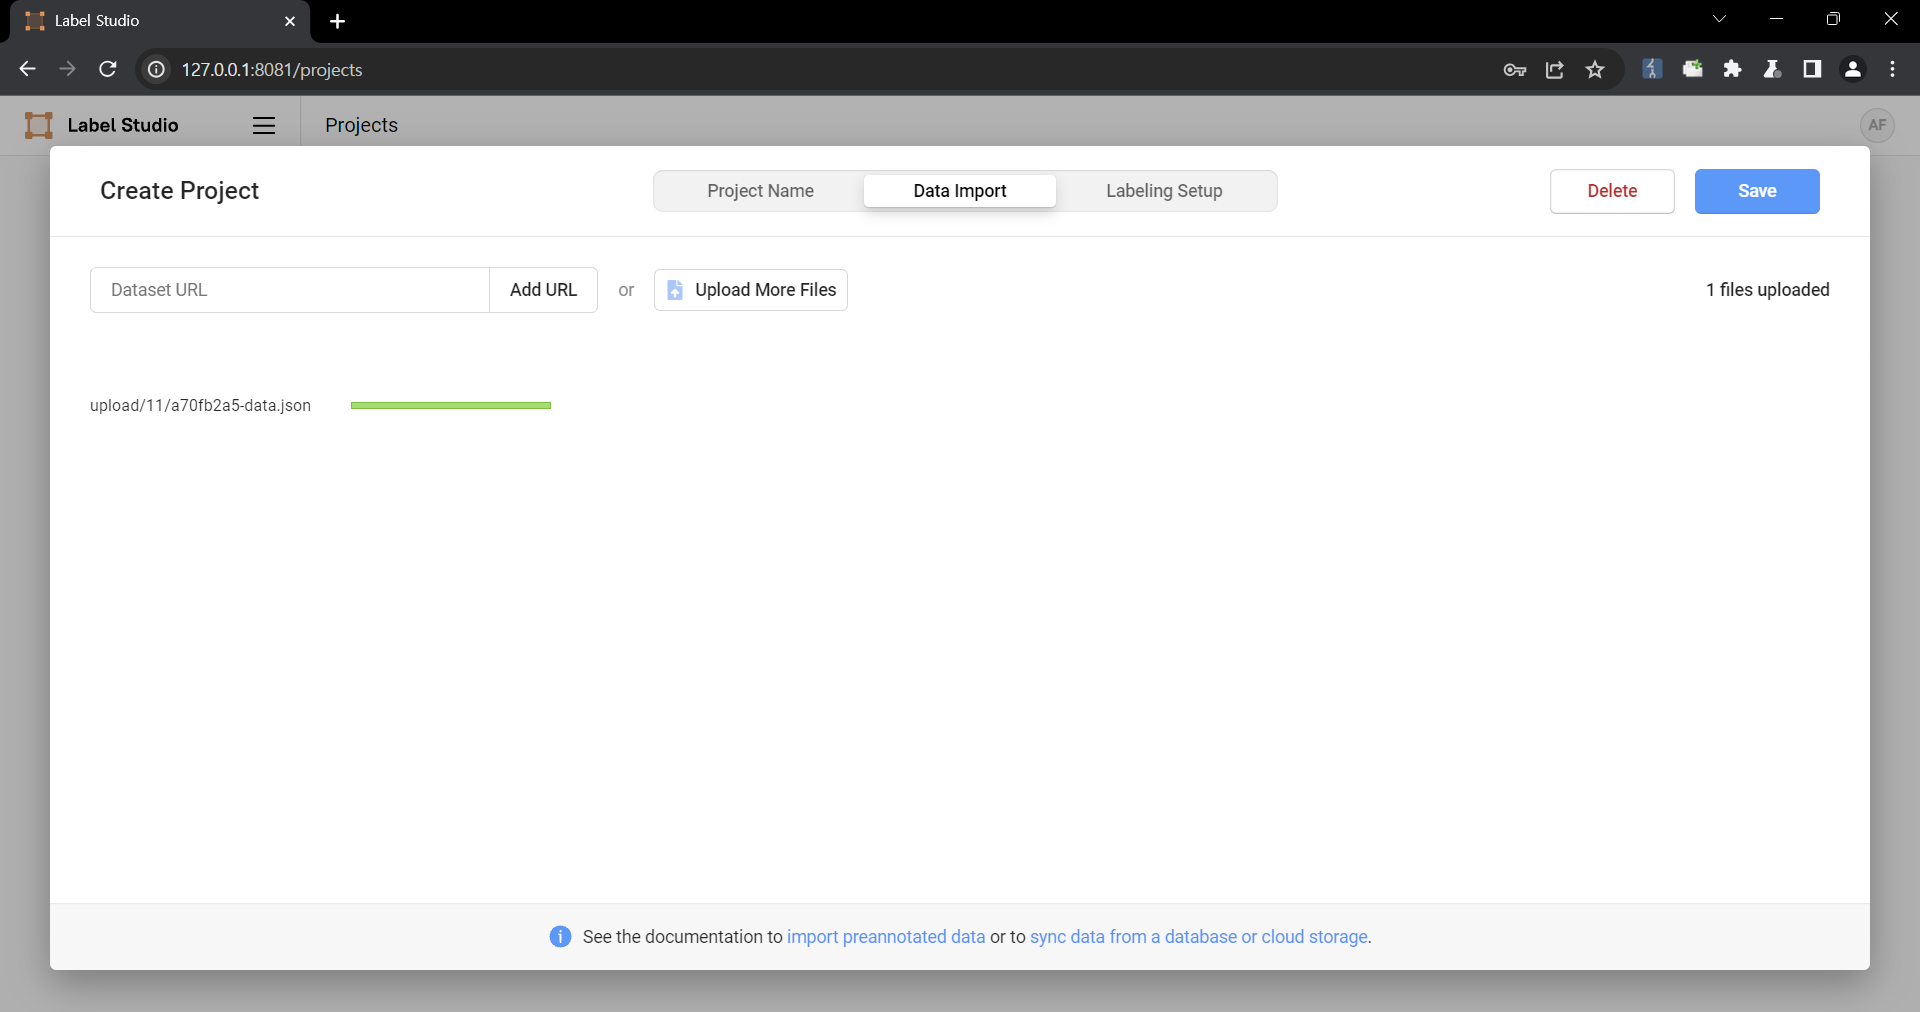 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 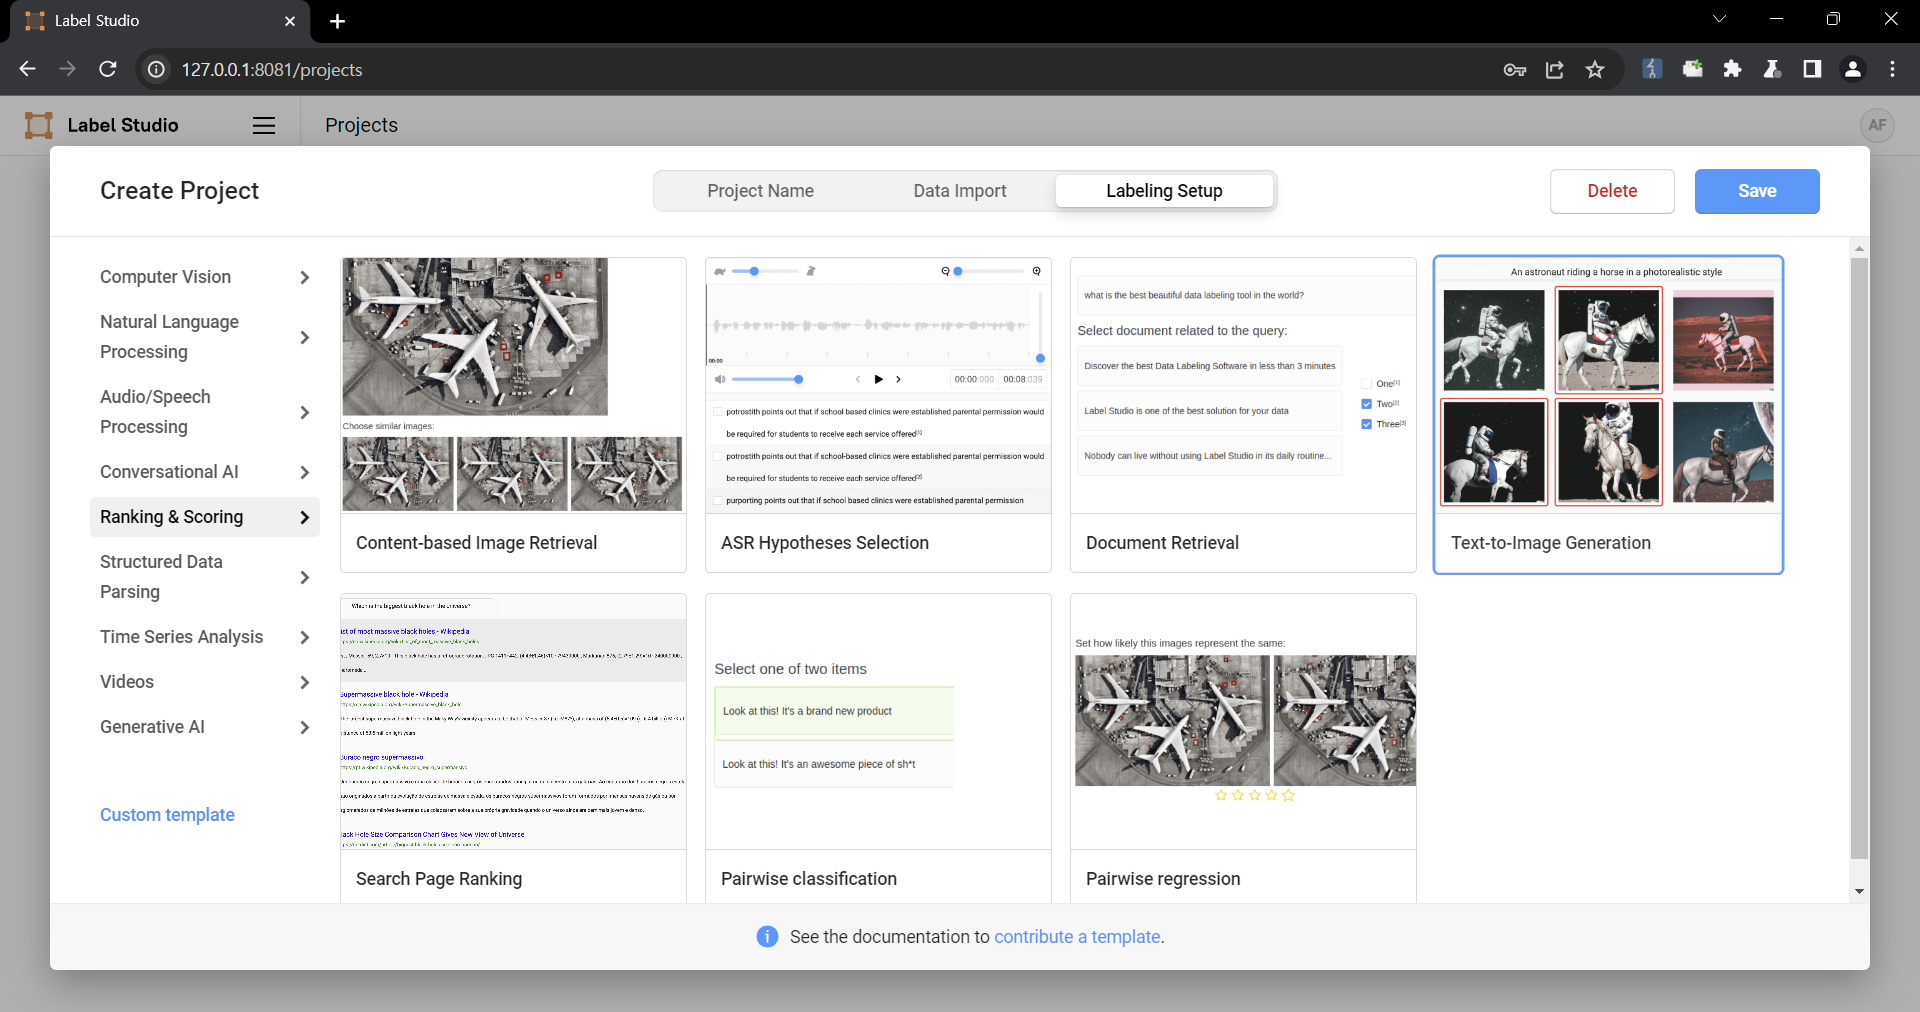 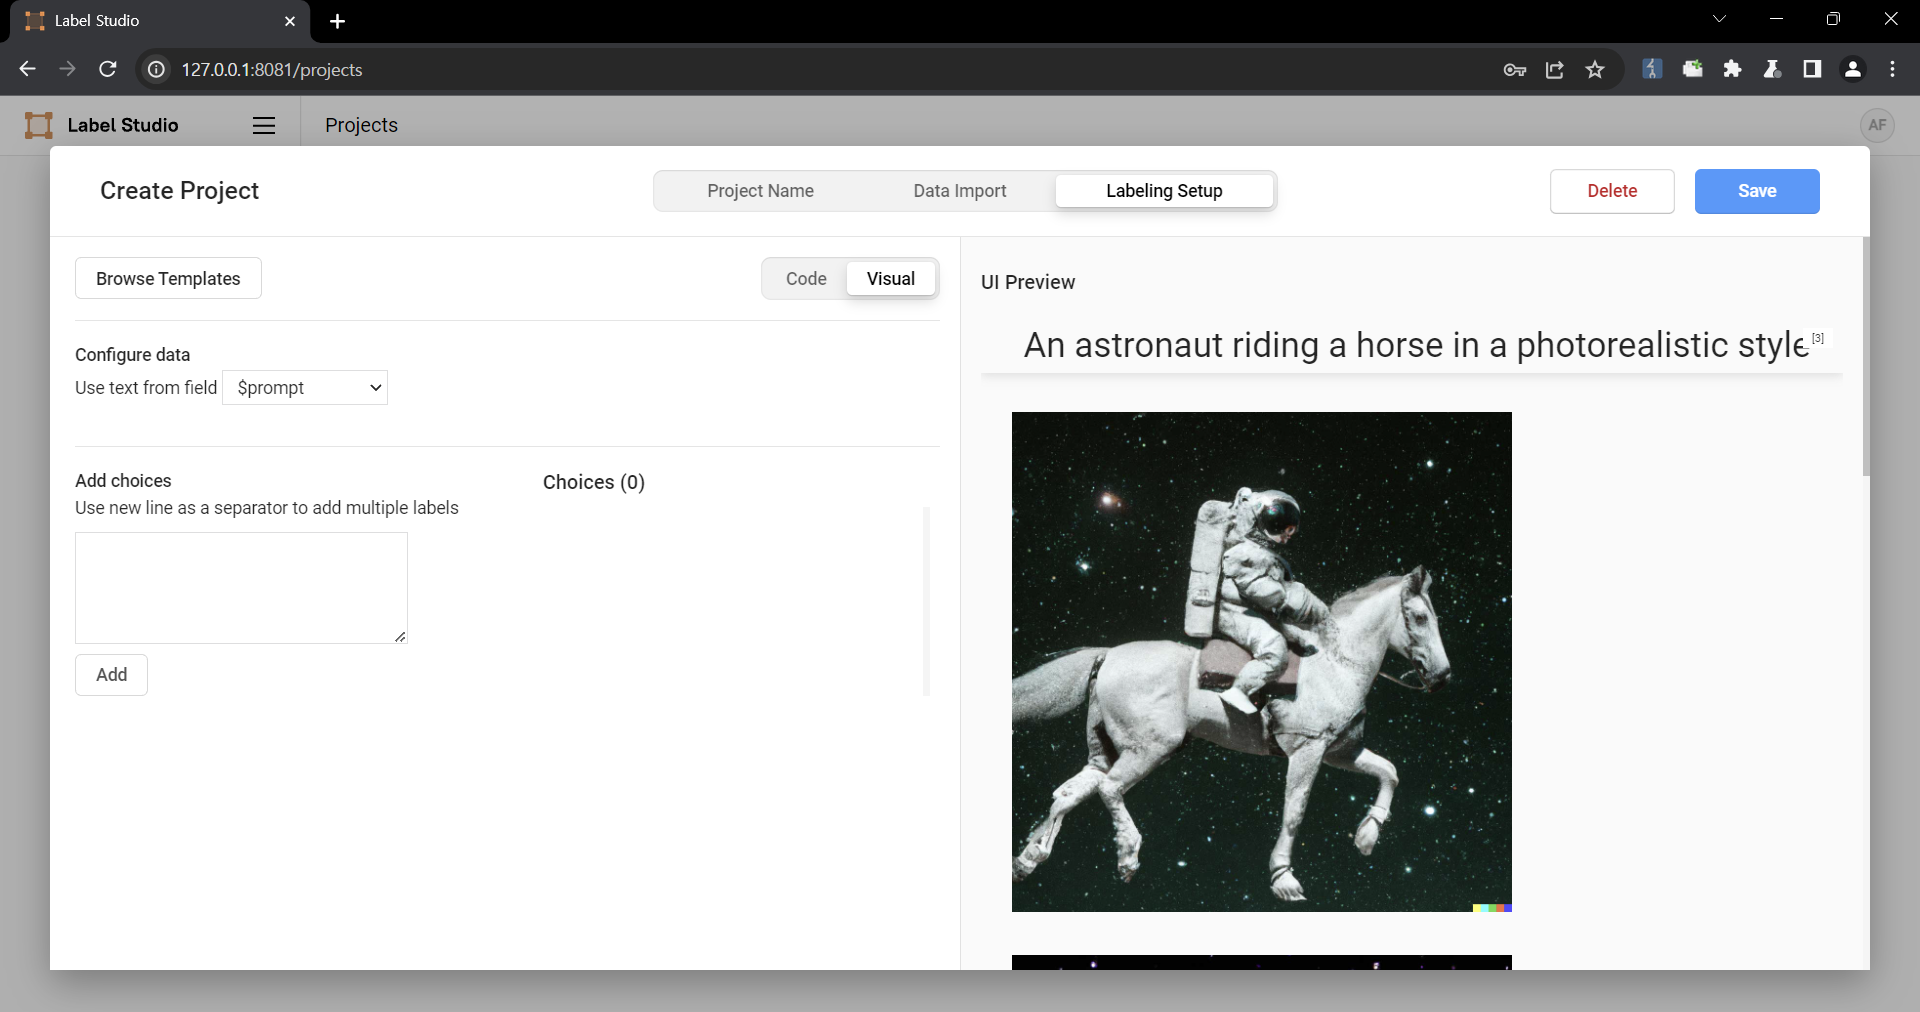 4. Select a task 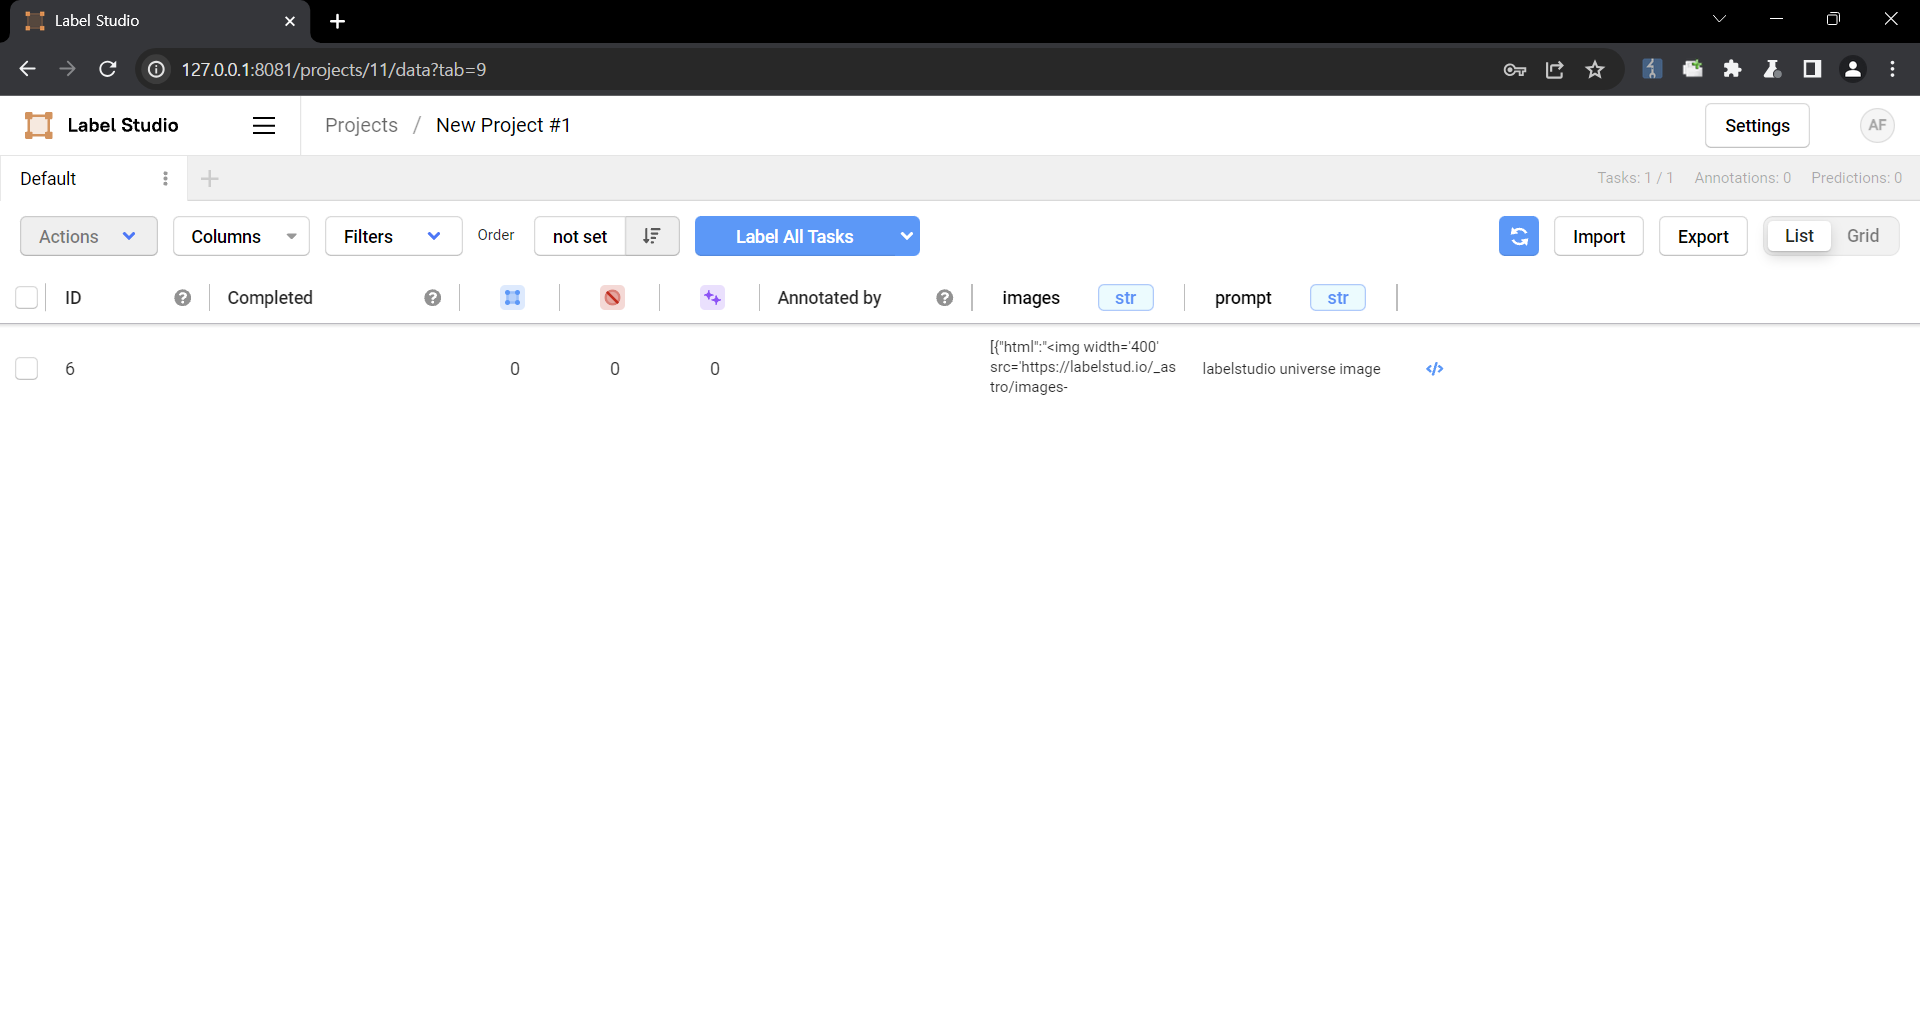 5. Check that the script is running 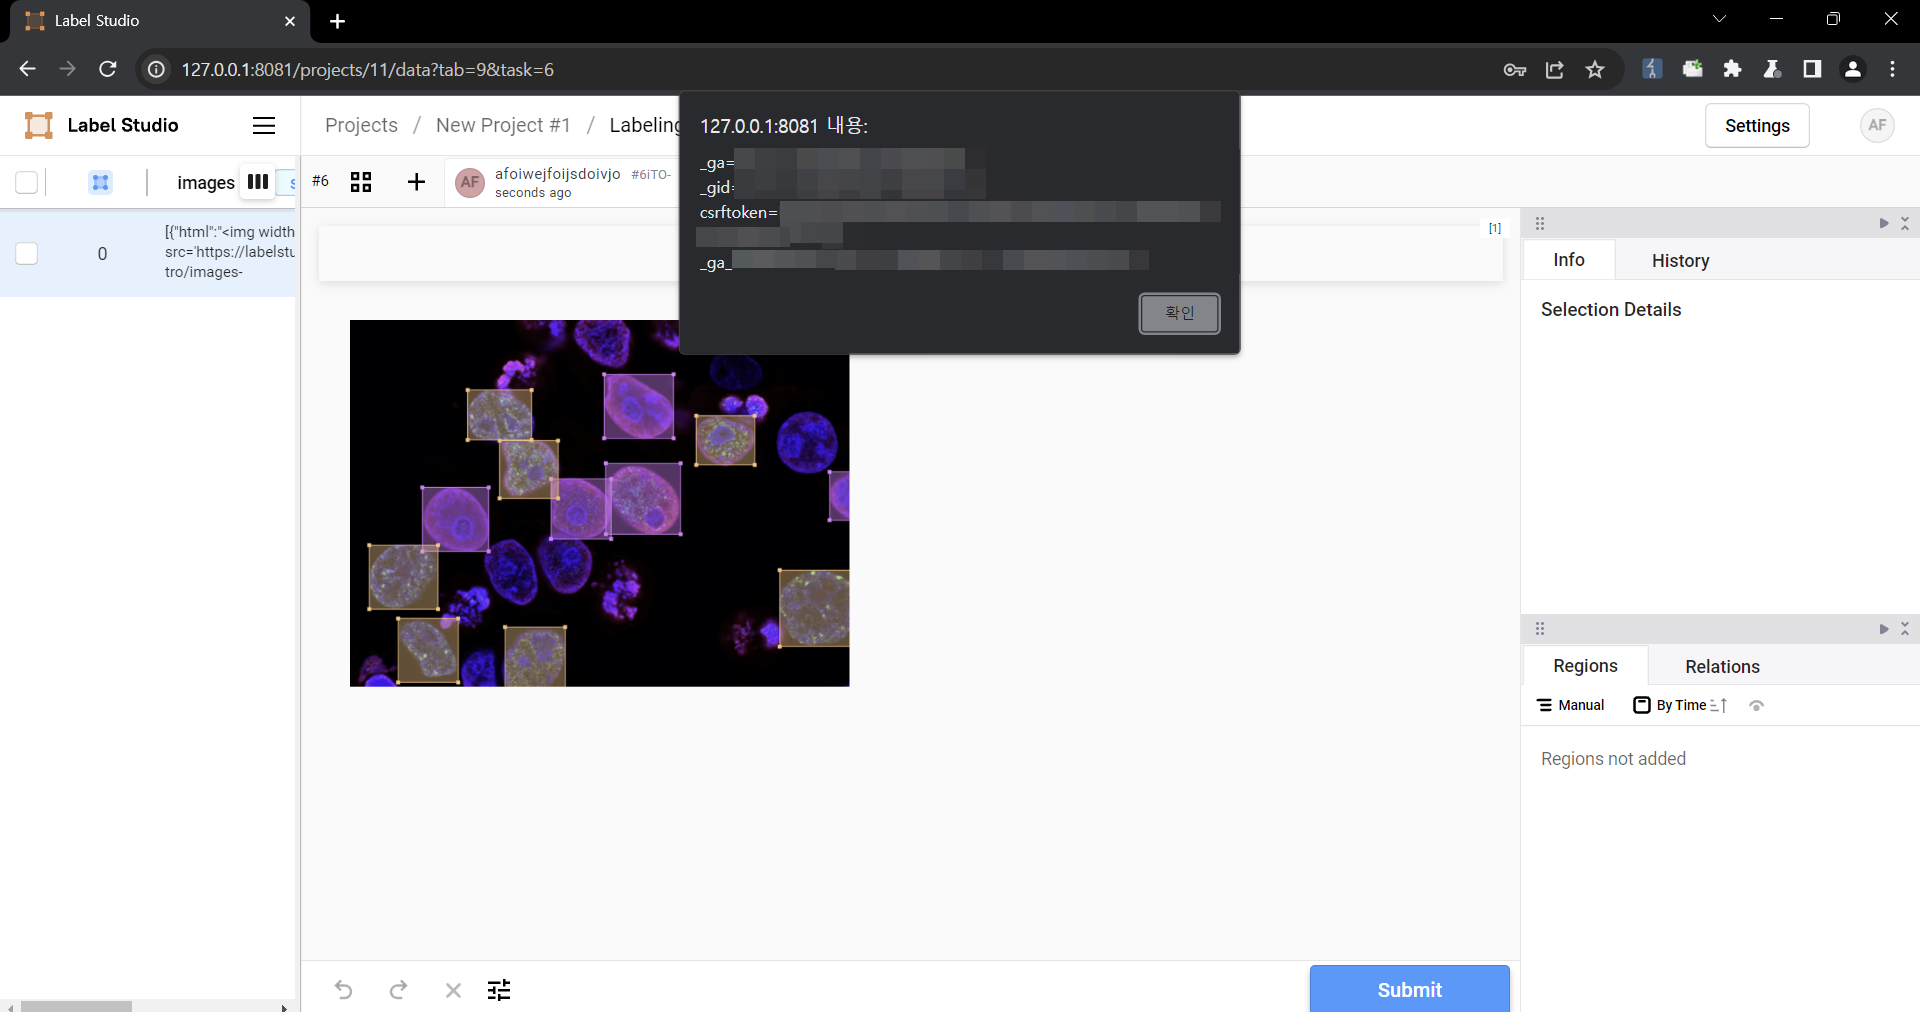 ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering. | ||||
| CVE-2022-34021 | 1 Resiot | 1 Iot Platform And Lorawan Network Server | 2025-05-16 | 5.4 Medium |
| Multiple Cross Site Scripting (XSS) vulnerabilities in ResIOT IOT Platform + LoRaWAN Network Server through 4.1.1000114 via the form fields. | ||||
| CVE-2024-46055 | 2 Davidguva, Openvidreview Project | 2 Openvidreview, Openvidreview | 2025-05-15 | 4.8 Medium |
| OpenVidReview 1.0 is vulnerable to Cross Site Scripting (XSS) in review names. | ||||
| CVE-2024-10473 | 2 Logichunt, Logo Slider Wordpress | 2 Logo Slider, Logo Slider Wordpress | 2025-05-15 | 5.4 Medium |
| The Logo Slider WordPress plugin before 4.5.0 does not sanitise and escape some of its Logo Settings when outputing them in pages where the Logo Slider shortcode is embed, which could allow users with a role as low as Author to perform Cross-Site Scripting attacks. | ||||
| CVE-2024-10493 | 2 Bdthemes, Element Pack Elementor Addons Wordpress | 2 Element Pack, Element Pack Elementor Addons Wordpress | 2025-05-15 | 5.4 Medium |
| The Element Pack Elementor Addons (Header Footer, Template Library, Dynamic Grid & Carousel, Remote Arrows) WordPress plugin before 5.10.3 does not validate and escape some of its block options before outputting them back in a page/post where the block is embed, which could allow users with the contributor role and above to perform Stored Cross-Site Scripting attacks. | ||||
| CVE-2022-35612 | 1 Bevywise | 1 Mqttroute | 2025-05-15 | 5.4 Medium |
| A cross-site scripting (XSS) vulnerability in MQTTRoute v3.3 and below allows attackers to execute arbitrary web scripts or HTML via a crafted payload injected into the dashboard name text field. | ||||
| CVE-2022-35134 | 1 Boodskap | 1 Iot Platform | 2025-05-15 | 5.4 Medium |
| Boodskap IoT Platform v4.4.9-02 contains a cross-site scripting (XSS) vulnerability. | ||||
| CVE-2025-4470 | 1 Senior-walter | 1 Online Student Clearance System | 2025-05-14 | 2.4 Low |
| A vulnerability classified as problematic was found in SourceCodester Online Student Clearance System 1.0. Affected by this vulnerability is an unknown functionality of the file /admin/add-student.php. The manipulation of the argument Fullname leads to cross site scripting. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. Other parameters might be affected as well. | ||||
| CVE-2025-22221 | 1 Vmware | 2 Aria Operations For Logs, Cloud Foundation | 2025-05-14 | 5.2 Medium |
| VMware Aria Operation for Logs contains a stored cross-site scripting vulnerability. A malicious actor with admin privileges to VMware Aria Operations for Logs may be able to inject a malicious script that could be executed in a victim's browser when performing a delete action in the Agent Configuration. | ||||
| CVE-2025-22219 | 1 Vmware | 2 Aria Operations For Logs, Cloud Foundation | 2025-05-14 | 6.8 Medium |
| VMware Aria Operations for Logs contains a stored cross-site scripting vulnerability. A malicious actor with non-administrative privileges may be able to inject a malicious script that (can perform stored cross-site scripting) may lead to arbitrary operations as admin user. | ||||
| CVE-2025-0794 | 1 Esafenet | 1 Cdg | 2025-05-13 | 3.5 Low |
| A vulnerability was found in ESAFENET CDG V5 and classified as problematic. Affected by this issue is some unknown functionality of the file /todoDetail.jsp. The manipulation of the argument curpage leads to cross site scripting. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. The vendor was contacted early about this disclosure but did not respond in any way. | ||||
| CVE-2022-43968 | 1 Concretecms | 1 Concrete Cms | 2025-05-13 | 6.1 Medium |
| Concrete CMS (formerly concrete5) below 8.5.10 and between 9.0.0 and 9.1.2 is vulnerable to Reflected XSS in the dashboard icons due to un-sanitized output. Remediate by updating to Concrete CMS 9.1.3+ or 8.5.10+. | ||||
| CVE-2022-43967 | 1 Concretecms | 1 Concrete Cms | 2025-05-13 | 6.1 Medium |
| Concrete CMS (formerly concrete5) below 8.5.10 and between 9.0.0 and 9.1.2 is vulnerable to Reflected XSS in the multilingual report due to un-sanitized output. Remediate by updating to Concrete CMS 9.1.3+ or 8.5.10+. | ||||
| CVE-2022-43695 | 1 Concretecms | 1 Concrete Cms | 2025-05-13 | 4.8 Medium |
| Concrete CMS (formerly concrete5) below 8.5.10 and between 9.0.0 and 9.1.2 is vulnerable to Stored Cross-Site Scripting (XSS) in dashboard/system/express/entities/associations because Concrete CMS allows association with an entity name that doesn’t exist or, if it does exist, contains XSS since it was not properly sanitized. Remediate by updating to Concrete CMS 9.1.3+ or 8.5.10+. | ||||
| CVE-2024-13328 | 1 Tanng | 1 Giga Messenger | 2025-05-13 | 6.1 Medium |
| The Giga Messenger WordPress plugin through 2.3.1 does not sanitise and escape a parameter before outputting it back in the page, leading to a Reflected Cross-Site Scripting which could be used against high privilege users such as admin | ||||
| CVE-2024-13330 | 1 Canaveralstudio | 1 Justrows Free | 2025-05-13 | 7.1 High |
| The JustRows free WordPress plugin through 0.2 does not sanitise and escape a parameter before outputting it back in the page, leading to a Reflected Cross-Site Scripting which could be used against high privilege users such as admin | ||||